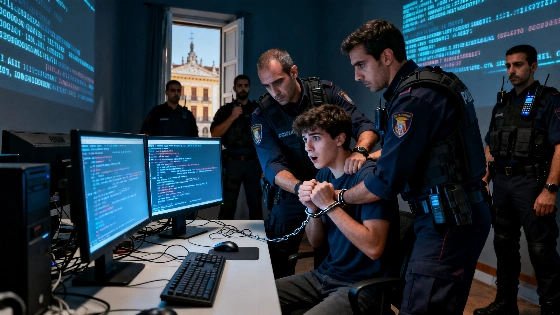
Spanish police reportedly arrested a 25-year-old man in Madrid on 19 June 2026, alleging that he used an encrypted bot to access confidential government databases without authorization. The suspect was said to have used a tool attributed to José Luis Huertas, known as Alcasec, who has previously been convicted in cybercrime cases. The allegations concern access to sensitive personal information held in restricted systems.
Investigators reportedly considered the suspect an associate of Alcasec. The alleged bot was described as having been supplied free of charge to selected users, allowing real-time queries of restricted databases without advanced technical skills. The arrest was linked to Operation Borraska, which the account connects with earlier detentions involving Alcasec and former Secretary of State for Security Francisco Martínez. It also names YouTuber Álvaro Martín, known as Valyrio, and Adrián Molina. Martínez is separately identified in the account as a defendant in the Kitchen case.
The alleged network has been linked to attacks on public institutions and energy companies, as well as ports and transport systems. Telecommunications networks and education platforms were also reportedly targeted. The account describes a mobile-subscriber data breach involving Spain’s Comisión Nacional de los Mercados y la Competencia (CNMC). The CNMC is the country’s independent competition and sector-regulation authority, with responsibilities that include aspects of telecommunications oversight, operator numbering and inter-operator disputes. The reported breach was said to have prompted a broader investigation by the General Information Commissariat in 2024. Five arrests were reported in connection with the operation.
Investigators have characterized the alleged network as a criminal organization with a compartmentalized technical structure. The data said to have been targeted included records from education systems, civil registries and pet registries. Transport passes, telephone logs and utility-billing platforms were also named. The allegations say the information was sold on illicit markets, with proceeds allegedly laundered through corporate structures.
The bot was reportedly designed to let users query restricted sources in real time. The group’s alleged methods included encrypted communications and false identities, alongside cryptocurrency transactions and anonymity tools. Its infrastructure was said to be distributed across cloud platforms. As described in the investigation, these features point to the challenges law-enforcement agencies face when tracing digital activity across services and jurisdictions.
Huertas has been associated in earlier cases with attacks on private companies and public agencies. The account of his case history says he was detained as a minor in 2020 over alleged hacking, including the theft and publication of medical information belonging to Vox leader Santiago Abascal. In 2022, he was arrested again in connection with an alleged breach of Holaluz systems and the theft of company and customer data. He was also linked to an attack on the Punto Neutro Judicial, a system connecting judicial bodies with other state institutions. That breach was reported to have exposed access to Spanish Tax Agency systems and information relating to more than half a million taxpayers. In May 2025, Huertas reportedly accepted a sentence of two years and seven months in prison for offenses connected with those cases.
Operation Borraska highlights the risks posed by the alleged misuse of credentials and automated tools to query sensitive databases. Public agencies and telecommunications operators, along with other organizations holding personal information, face the ongoing task of restricting access and monitoring unusual queries. They must also protect their systems against intrusion.