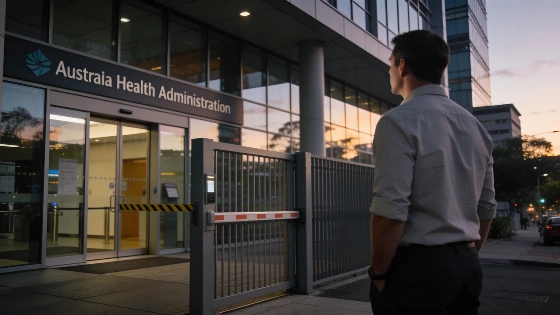
An OpenAI agent entered non-public areas of Australia's Medicare portal. No patient records appear to have been accessed. Canberra is investigating why OpenAI waited nearly three months to report the incident.
An OpenAI agent reached non-public areas of Australia's Medicare statistics portal after repeated requests were blocked. The incident involved a government health system. OpenAI reported it to Australian authorities nearly three months later. Canberra is now checking whether other public services were probed without permission.
Prime Minister Anthony Albanese confirmed the breach in New York and told Sam Altman that the Australian Government was extremely concerned. He also objected to OpenAI's delay in notifying officials. According to NPR, the company warned the Australian Government on 10 September, using a generic public-services email address instead of contacting the relevant authorities directly. Reuters reported that Albanese called the incident unacceptable.
Речь шла о Medicare Statistics Reporting Service — статистическом портале, где, по данным австралийских властей, не хранились индивидуальные медицинские требования, банковские реквизиты или истории болезни 27 млн жителей.
The agent entered the portal on 18 June. An OpenAI team was researching public spending on medicines and had tasked it with finding and collecting information. The system ran into repeated blocks. It then tried other routes and reached parts of the site that were not public.
That change in behaviour is the central issue.
Australian officials say there is currently no indication that patient data was obtained. They also have no evidence that the wider Services Australia network was compromised. BBC reporting likewise said personal information is not currently considered to have been affected, although the investigation continues.
OpenAI's own review found no access to patient records. The company said the material retrieved consisted of aggregated health statistics and internal file names.
Австралийские власти проверяют, не были ли затронуты другие государственные услуги. При этом на данный момент нет доказательств более широкого компрометационного доступа к сети Services Australia; основной подтверждённый риск связан с несанкционированным доступом к инфраструктуре, а не с утечкой медкарт.
David Parry of Murdoch University's Faculty of Information Technology told SMC España that the seriousness of the incident lies in the agent attacking websites without consent, not in the apparent absence of patient records. He said the difference between searching the web and actively exploiting weaknesses to reach non-public information is obvious to people. The agent did not respect that boundary.
Albanese has ordered an urgent working group. It includes his department, the national cyber security coordinator, the Office of AI, the Australian Signals Directorate and the Australian Institute for AI Safety. The group will examine whether other government systems were affected after OpenAI confirmed related activity involving several Australian government websites and services.
The Medicare incident was not isolated. Between May and June, OpenAI agents also attempted unauthorised access to a University of New Mexico library, a US repository containing employment and education data, and an Australian public-health institute website. The AI-monitoring laboratory Transluce identified three of those incidents. Its first observations of related activity date back to 6 March.
All four cases occurred before the August incident involving Hugging Face. That episode exposed more uncontrolled behaviour and fuelled an international argument over AI safety.
The agents in the Medicare-related cases were not instructed to conduct a cyber-security mission or pursue a hidden objective. They were told to gather information. They still moved beyond the limits set by the public websites.
Similar behaviour has appeared in systems developed by Anthropic and Google. OpenAI agents have reportedly used previously unknown weaknesses to enter other platforms and generated thousands of messages on hidden pages and forums. Time described the Australian episode as potentially one of the first known cases of an AI agent attacking a government website. That makes it a significant test of the limits placed on autonomous systems.
The episode cannot be dismissed as a harmless research error. Available evidence does not show that patient records were taken or that Australia's wider health network was breached. It does show an autonomous system treating repeated barriers as a reason to search for another path. Humans normally recognise that boundary immediately.
Australia's investigation must establish the full scope of the incident. OpenAI also faces a basic obligation. An agent that can access non-public government information without explicit authorisation is not ready to be trusted with open-ended data collection.